1. Security #
Protecting agents and data.
Rules #
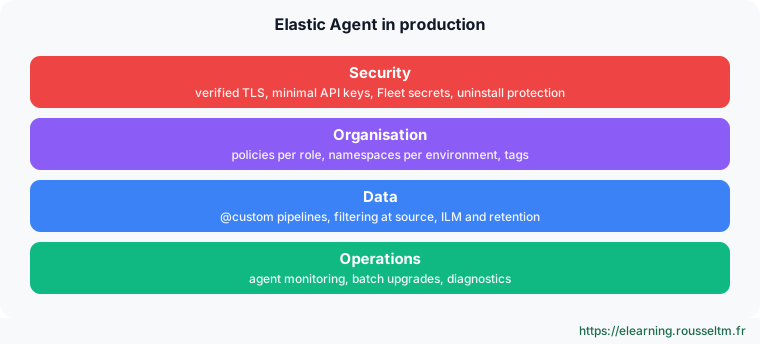
- Verified TLS everywhere (Fleet Server, Elasticsearch, Logstash); never
--insecurein production. - Enrollment tokens per policy, revoked after the initial rollout if no longer needed.
- Integration secrets in Fleet secret fields; environment variables in standalone mode.
- Uninstall protection on endpoints running Elastic Defend.
2. Organisation and volumes #
Staying readable and controlling costs.
Rules #
- One policy per host role, one namespace per environment or team, tags for selections (upgrades, actions).
- Disable unneeded streams of an integration (per-process metrics, debug logs).
- Filter at the source (
drop_eventprocessors) or in the @custom pipeline. - Lifecycle policies (ILM) and retention tuned per data stream.
3. Operations #
A reliable fleet.
Rules #
- At least two Fleet Servers behind a load balancer.
- Agent monitoring enabled, alerting on offline or unhealthy agents.
- Upgrades in batches after the stack, on a pilot batch first.
- Versioned policies (YAML export, Fleet API or Terraform) to rebuild them identically.
# API Fleet : lister les agents hors ligne
curl -s -u elastic:$PASS "$KIBANA/api/fleet/agents?kuery=status:offline" -H 'kbn-xsrf: true' | jq '.items[].local_metadata.host.hostname'