1. Security #
Protecting agents and data.
Rules #
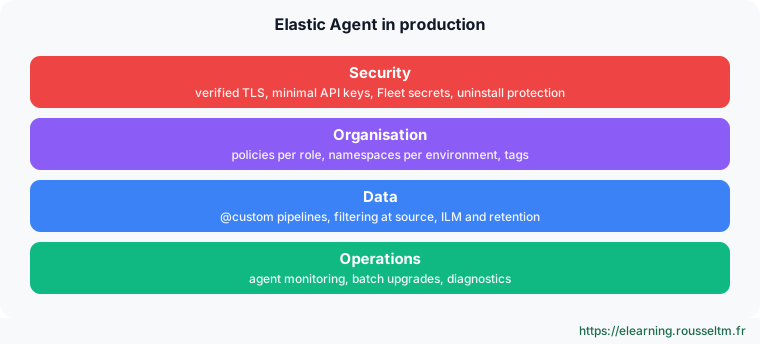
- Verified TLS everywhere (Fleet Server, Elasticsearch, Logstash); never
--insecurein production. - Enrollment tokens per policy, revoked after the initial rollout if no longer needed.
- Integration secrets in Fleet secret fields; environment variables in standalone mode.
- Uninstall protection on endpoints running Elastic Defend.
2. Organisation and volumes #
Staying readable and controlling costs.
Rules #
- One policy per host role, one namespace per environment or team, tags for selections (upgrades, actions).
- Disable unneeded streams of an integration (per-process metrics, debug logs).
- Filter at the source (
drop_eventprocessors) or in the @custom pipeline. - Lifecycle policies (ILM) and retention tuned per data stream.
3. Operations #
A reliable fleet.
Rules #
- At least two Fleet Servers behind a load balancer.
- Agent monitoring enabled, alerting on offline or unhealthy agents.
- Upgrades in batches after the stack, on a pilot batch first.
- Versioned policies (YAML export, Fleet API or Terraform) to rebuild them identically.
# API Fleet : lister les agents hors ligne
curl -s -u elastic:$PASS "$KIBANA/api/fleet/agents?kuery=status:offline" -H 'kbn-xsrf: true' | jq '.items[].local_metadata.host.hostname'My progress
Sign in to track your progress and take notes. Sign in
💬 Questions about this lesson
No questions yet: be the first to ask for help or share your configuration.
Recommended Articles
Elastic Agent: architecture, Fleet and integrations
Understand Elastic Agent: single collection agent, Fleet and Fleet Server, agent policies, integr...
Installing Fleet Server and enrolling Elastic Agents
Set up Fleet Server, create a policy, enroll Linux, Windows and Docker agents, understand tokens ...
Elastic Agent or Beats? Choosing and migrating
Compare Elastic Agent and Beats (Filebeat, Metricbeat, Winlogbeat), know when to keep Beats, and ...
Elastic Agent on Kubernetes
Deploy Elastic Agent on Kubernetes: Fleet-managed DaemonSet, Kubernetes integration, kube-state-m...
Standalone Elastic Agent, Logstash and Kafka outputs, and OpenTelemetry (EDOT)
Write a standalone configuration, ship to Logstash or Kafka, and use Elastic Agent as an OpenTele...
Monitoring, upgrading and troubleshooting Elastic Agent
Operate an Elastic Agent fleet: states in Fleet, agent monitoring, batch upgrades, diagnostics, l...
Agent policies, integrations, data streams and pipelines
Build agent policies, add integrations (System, Nginx, Custom Logs), choose namespaces, customise...
Elastic Observability: logs, infrastructure, APM and synthetics
Elastic Observability features: log exploration, infrastructure inventory with Elastic Agent and ...
Beats: going further (security, performance, Elastic Agent and migrating to Alloy)
Industrialize Filebeat, Metricbeat and the other Beats: secure outputs, processors, modules, tuni...