1. Filters #
Transforming events.
Essential filters #
| Filter | Role |
|---|---|
| mutate | rename, convert, remove, add fields |
| date | set @timestamp from a date field |
| json / kv | decode JSON or key=value pairs |
| drop | drop useless events |
| fingerprint | compute a stable ID |
filter {
  json   { source => "message" skip_on_invalid_json => true }
  date   { match => ["time", "ISO8601"] remove_field => ["time"] }
  mutate {
    rename  => { "lvl" => "[log][level]" }
    convert => { "[http][response][status_code]" => "integer" }
  }
  if [url][path] == "/health" { drop {} }
}
2. The grok plugin #
Named patterns.
Principle #
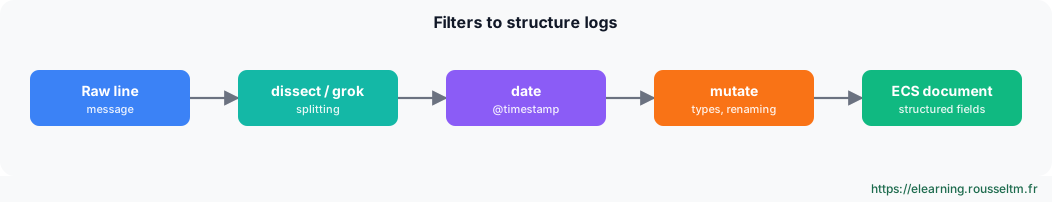
grok maps named regular expressions to fields: %{IP:[source][ip]} captures an IP address into source.ip. More than 120 patterns are provided (IP, NUMBER, TIMESTAMP_ISO8601, COMBINEDAPACHELOG…).
# 2026-11-09T10:15:00Z ERROR 203.0.113.7 GET /api/commande 500 132ms
grok {
  match => { "message" => "%{TIMESTAMP_ISO8601:ts} %{LOGLEVEL:[log][level]} %{IP:[source][ip]} %{WORD:[http][request][method]} %{URIPATH:[url][path]} %{NUMBER:[http][response][status_code]:int} %{NUMBER:duree_ms:int}ms" }
}
Good practice: Build your patterns with the Kibana Grok Debugger (Dev Tools) and anchor them (^…$): an unanchored pattern that fails scans the whole line and costs a lot of CPU.Common mistake: Ignoring the _grokparsefailure tag: unmatched lines are shipped without structure and skew dashboards. Monitor it and send those events to a separate data stream.3. dissect or grok? #
Choosing the right tool.
dissect #
dissect splits the line on fixed delimiters, without regular expressions: it is much faster, but cannot handle a variable format.
dissect {
  mapping => { "message" => "%{ts} %{[log][level]} %{[source][ip]} %{[http][request][method]} %{[url][path]} %{[http][response][status_code]} %{duree}" }
}| dissect | grok | |
|---|---|---|
| Method | delimiters | regular expressions |
| Performance | very fast | more costly |
| Variable format | no | yes (alternatives, optional parts) |
| Typing | with mutate or convert_datatype | in the pattern (:int) |
Good practice: Combine both: dissect for the fixed header of the line, grok only on the variable part.
