1. What is Vulnerabilities for? #
Detect vulnerabilities actually exploitable at runtime, third-party and in your code.
The principle #
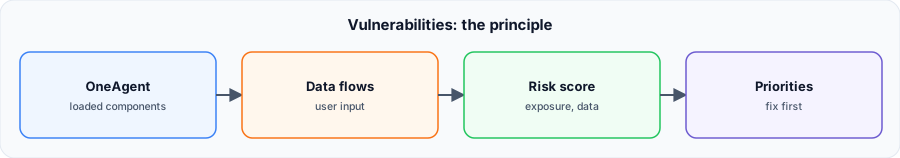
The Vulnerabilities app relies on Runtime Vulnerability Analytics: it analyzes what is running, not only what is deployed. A vulnerability is only reported if the component is loaded. It covers third-party and open source libraries, as well as in-house code.
2. Key features #
What the app offers.
Overview #
| Feature | Role |
|---|---|
| Vulnérabilités tierces | Component names and versions matched against vulnerability feeds |
| Vulnérabilités du code | Runtime code inspection and user input tracking (OneAgent 1.259+) |
| Contexte | Public exposure, data access, affected entity |
| Remplacement | The former Third-Party and Code-Level Vulnerabilities apps are deprecated |
3. Getting started #
First steps.
Step by step #
- Enable detection in Settings > Application Security > Vulnerability Analytics.
- Open Vulnerabilities and sort by risk.
- Check whether the component is exposed and touches data.
- Fix, then track resolution.
Prerequisites #
- Deep monitoring enabled on processes.
- Bundlers such as Webpack hide components: detection decreases.
Prioritize. A critical vulnerability in a never-loaded library weighs less than a medium one exposed on the Internet: that is the point of runtime analysis.
Sources #
From the official documentation consulted in November 2026: labels and availability change with platform versions.
